Initial Situation
While data is now frequently encrypted during transmission and storage, it usually must be available in RAM for traditional processing. This allows individuals or attackers with extensive system privileges to potentially access sensitive data or processes. For applications requiring high levels of protection, this creates a gap between data in transit, data at rest, and data in use.
The SCS Contribution
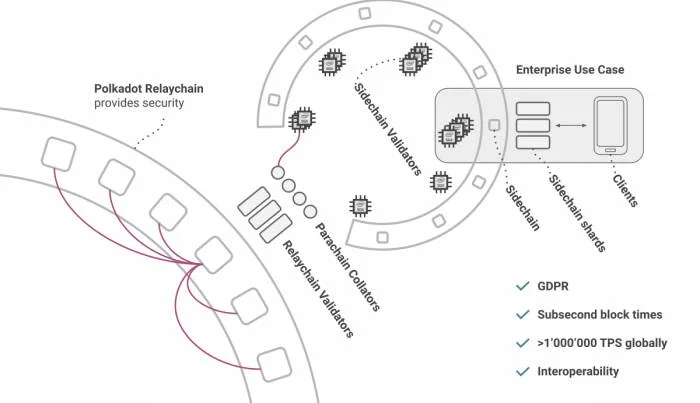
On behalf of Integritee, Web3 Foundation, and Polkadot Council, SCS developed a framework that combines Trusted Execution with blockchain technology and significantly reduces technical complexity for developers.
Result
The developed framework combines the confidentiality of hardware-backed Trusted Execution Environments with the public traceability of a blockchain. This enables developers to build applications where sensitive raw data remains protected during processing and the execution environment used is cryptographically verifiable. This allows for the implementation of “Security by Design” without having to expose sensitive processing to the operator infrastructure.
Data in Use
Sensitive data protected even during processing.
Remote Attestation
Execution environment and program state cryptographically verifiable.
TEE-Validated Sidechains
Confidential processing with a publicly traceable basis of trust.